OWASP Bug Logging Tool
Find it. Report it. Fix it. Get rewarded. OWASP BLT is a community-built family of 47 open-source tools that lets anyone report bugs and vulnerabilities on any website, app or repository, rewards the people who find them, and turns newcomers into security contributors.
About OWASP Bug Logging Tool
OWASP BLT (Bug Logging Tool) lets everyone who uses the internet help make it better. Spot a broken link, a typo, a 500 error or a serious vulnerability on any website, app or repository, and log it on BLT. Public issues are verified by the community, security issues are disclosed privately, and the organizations involved are held to account until they're fixed.
What started in 2012 as an idea to make a game out of bug finding has grown into a family of 47 open-source projects, built by 350 contributors in more than 46,000 commits. All of it is free and open source at git.owaspblt.org/BLT.
🐛 Report anything. Log any bug, with screenshots, from the web, the mobile app, the browser extension, the terminal or an AI agent.
🔒 Disclose responsibly. Send sensitive findings through BLT Zero's encrypted, zero-log channel. Accepted vulnerabilities can get an ID in the BLT-YYYY-NNNN registry.
🏆 Reward the finders. Earn points, climb leaderboards, win bug hunts and hackathons, and get recognized for every fix.
🎓 Grow security talent. Take free courses and browser labs at BLT University, make a guided first contribution, and join a mentored Google Summer of Code project.
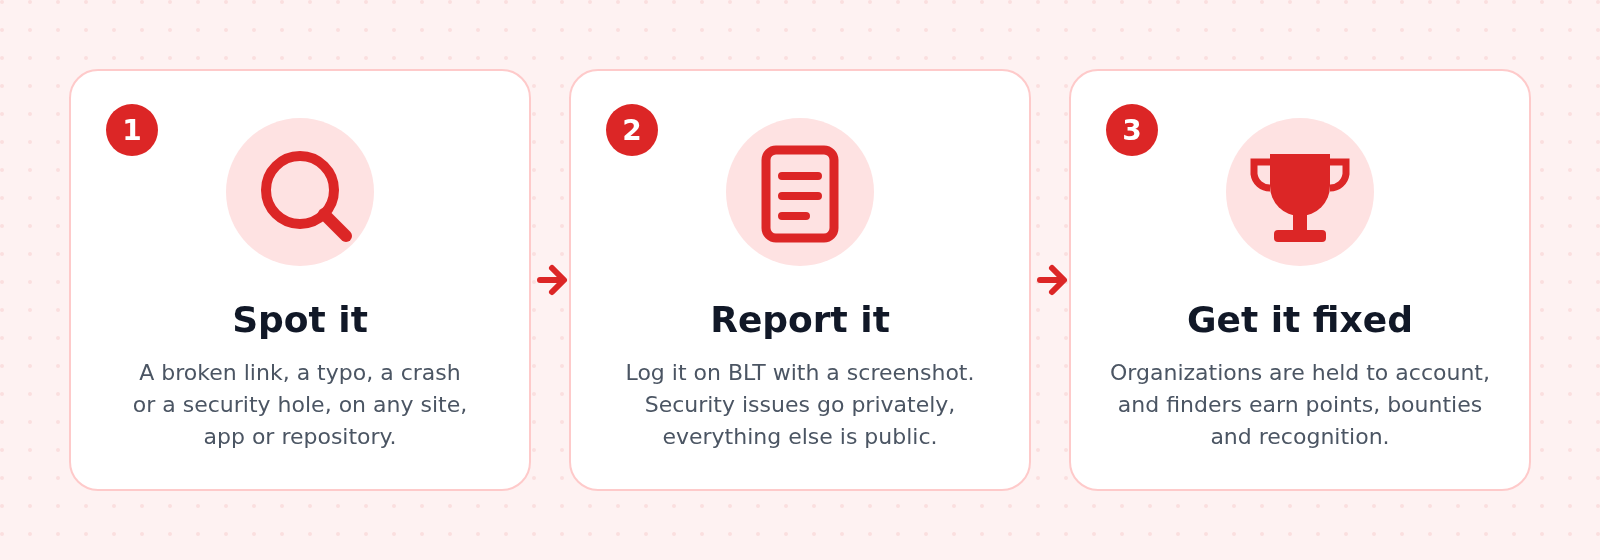
For bug hunters
Spot something wrong on any site, app or repository.
Log it on owaspblt.org with a description and a screenshot. Security issues go privately.
Earn points, bounties and recognition as it gets verified and fixed.
For organizations
Claim your domain and see every report about it in one place.
Launch a bug hunt with a prize pool, or a hackathon for your contributors.
Fix what's reported and give your users a bug-free experience.
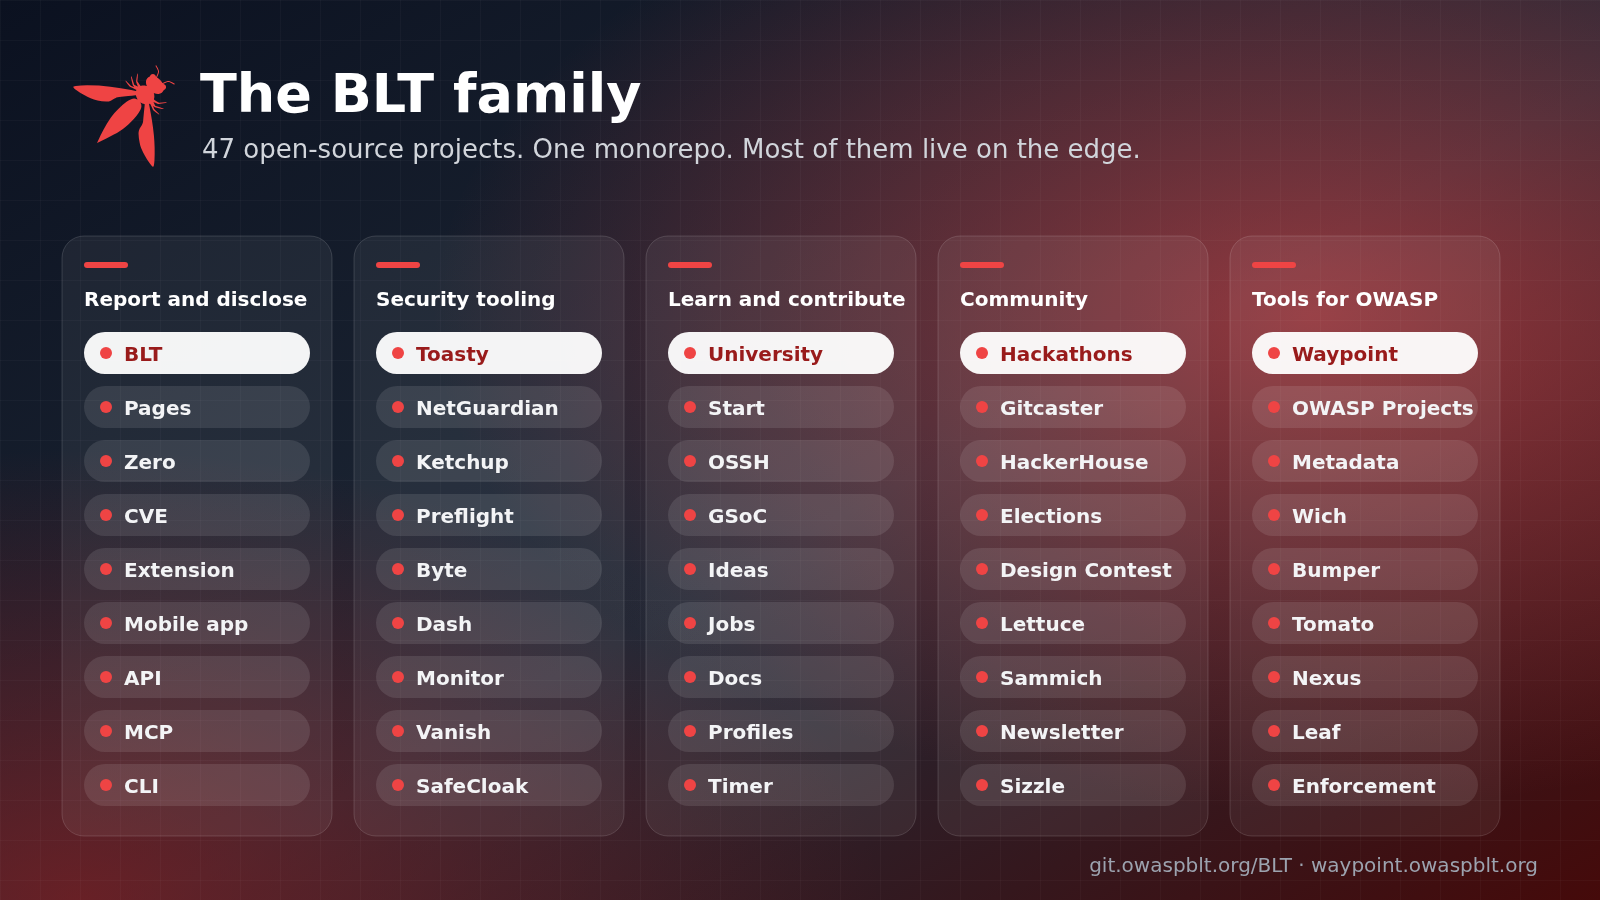
Every BLT project lives in one open monorepo at git.owaspblt.org/BLT, and most run live on the edge. Here are the highlights.
🐞 Report and disclose
BLT: the main platform for gamified, crowd-sourced bug reporting and vulnerability disclosure
BLT Pages: public bug reports, leaderboard and community elections
BLT Zero: zero-trust, encrypted vulnerability reporting
BLT CVE: a community vulnerability registry under the BLT-YYYY-NNNN namespace
Extension, mobile app, API and MCP server: report from your browser, your phone, your code or your AI agent
🛡️ Security tooling
Toasty: AI triage that redacts secrets and PII, finds duplicates and summarizes reports
NetGuardian: distributed domain crawling and signed findings, with triage for organizations
Ketchup: a real-time workspace for penetration testing teams
Preflight: security guidance for contributors before they open a pull request
Vanish and SafeCloak: personal data removal and private peer-to-peer calls
🎓 Learn and contribute
BLT University: short courses, browser-based security labs and recent vulnerability data
Start and OSSH: a contributor start page, and an AI guide to the open-source project that fits you
GSoC, Ideas and Jobs: Google Summer of Code, project proposals and a security job board
🏅 Community
Hackathons: contributor hackathons with live charts, leaderboards and prizes
Gitcaster and HackerHouse: live repository activity, with sportscaster-style commentary
🧭 Tools for OWASP
OWASP Projects and Metadata: status, issues and metadata for every OWASP project
Wich and Bumper: score a repository against 100 OWASP points, and nudge idle ones back to life
Lettuce: the Slack bot that welcomes new members to the OWASP community
BLT needs developers, and just as much it needs testers, writers, designers, researchers, translators and organizers. You don't need a security background to start.
🌱 Make your first pull request. Pick a good first issue and follow the contributing guide.
💬 Say hello. Join #project-blt on the OWASP Slack and ask anything.
🐛 Report a bug. Log it on owaspblt.org, or report a vulnerability privately through BLT Zero.
🗳️ Lead a project. Nominate yourself or someone else in the community elections.
October 2026: every BLT project moves into one monorepo, with its full history, at git.owaspblt.org. Read the story.
Summer 2026: eleven Google Summer of Code projects ship security tools, learning platforms and edge infrastructure.
2025: BLT 2.0 and 2.1 bring a full redesign, Slack integration, security labs, hackathons, bounty payouts and dark mode.
2024: a new home page, an AI chatbot, website monitoring and cryptocurrency payments.
May 2023: BLT becomes an OWASP Production project.
September 2016: BLT becomes an official OWASP project.
January 2012: the idea is born: a website that makes a game out of bug finding.
BLT has mentored Google Summer of Code contributors every year since 2020. In 2026, eleven contributors shipped working security tools, learning platforms and edge-native infrastructure. Meet the 2026 team.
Want to take part next year? Browse the project ideas, start contributing early, and find everything else on gsoc.owaspblt.org.
What is OWASP BLT?
A free, open-source set of tools for reporting bugs and vulnerabilities on any website, app or repository, rewarding the people who find them, and teaching security through real contributions.
Who can use it?
Anyone. You don't need a security background to report a broken page, and experienced researchers get private disclosure, bug hunts and bounties.
How do I report a security vulnerability?
Never in a public issue. Use BLT Zero for encrypted reports about any site. For vulnerabilities in BLT itself, follow the Security Policy.
Can my organization run a bug hunt?
Yes. Launch a bug hunt with a prize pool on owaspblt.org, or a contributor hackathon on BLT Hackathons.
Where is the code? Is GitHub still used?
All BLT code, issues and pull requests are at git.owaspblt.org/BLT. github.com/OWASP/BLT is a read-only mirror kept as a backup.
Is it free?
Yes. Each project keeps its own open-source license; most are AGPL-3.0.
I don't write code. Can I still help?
Absolutely. Testing, docs, design, research, translation, mentoring and organizing events all move the project forward.
BLT is a pro-AI project: coding agents and AI assistants are welcome for issues, pull requests, tests and docs. Every BLT issue has a one-line prompt you can paste into your agent to start work.
You stay responsible for the result: review every change and run the project's tests before you submit.
Every pull request names the AI model used, or says None.
Never paste secrets or private vulnerability details into AI services.
Read the full AI Policy before you contribute.
Donations to OWASP BLT pay for hosting, events and outreach, and keep every BLT tool free and open for everyone. Every contribution, however small, helps make the internet a little less buggy.
Project Resources
Project Leaders
Project Information
 Slack