Mobile Audit is a Django application for static application security testing and malware inspection. It extracts APK metadata, detects risky implementation patterns, organizes findings by severity, and provides a focused workspace for review and reporting.
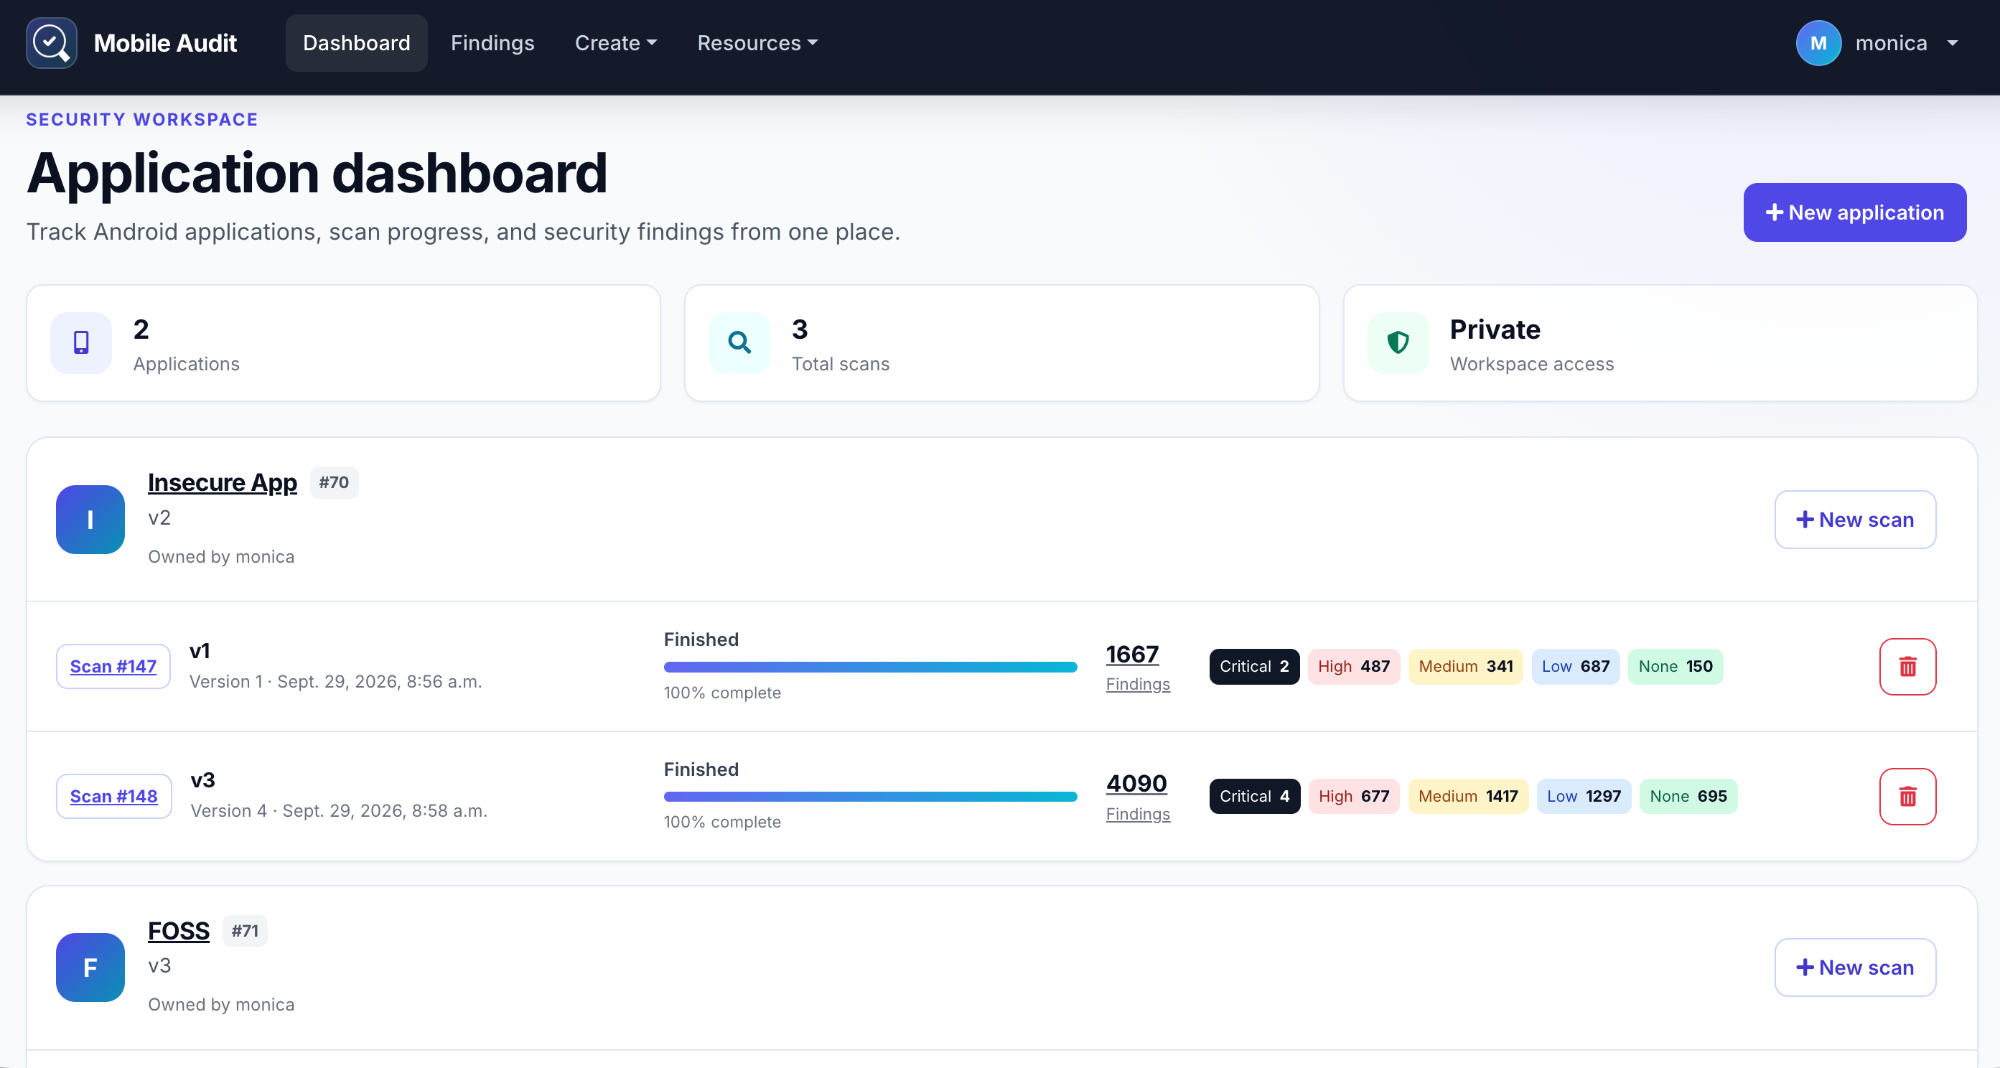
It is a containerized web application that automates security analysis of Android APK files. It decompiles APKs, extracts metadata, searches for security vulnerabilities using pattern matching, categorizes findings according to CWE standards and OWASP Mobile Top 10, and integrates with external threat intelligence services.
The platform is designed for security auditors, developers, and DevSecOps teams who need to perform comprehensive security assessments of Android applications. It provides both an interactive web interface and a REST API for programmatic access.
It checks if there has been an scan of the APK and extract all its information. Also, there is the possibility of uploading the APK is selected a property in the environment (Disabled by default).
It checks in the database if there are URLs in the APK that are related with Malware.
If you are interested in contributing with Mobile Audit: https://github.com/mpast/mobileAudit/blob/main/CONTRIBUTING.md
Project Leaders
Monica Pastor Abanades
Project Leader
Project Information
 Slack